Snyk Alternatives for Developer Security: SCA, SAST, Container and IaC Scanning
Snyk made developer-first security popular: scan your dependencies, code, containers and infrastructure-as-code from the IDE, the CLI and every pull request. But its free plan has tight test limits, its enterprise plan now runs on prepaid credits, and many teams want a cheaper bundle, an open-source scanner or a tool built into GitHub or GitLab. This guide compares 16 Snyk alternatives for SCA, SAST, container and IaC scanning, from all-in-one platforms to free open-source tools. We checked every free plan and price on the vendor's official pricing page in November 2026.
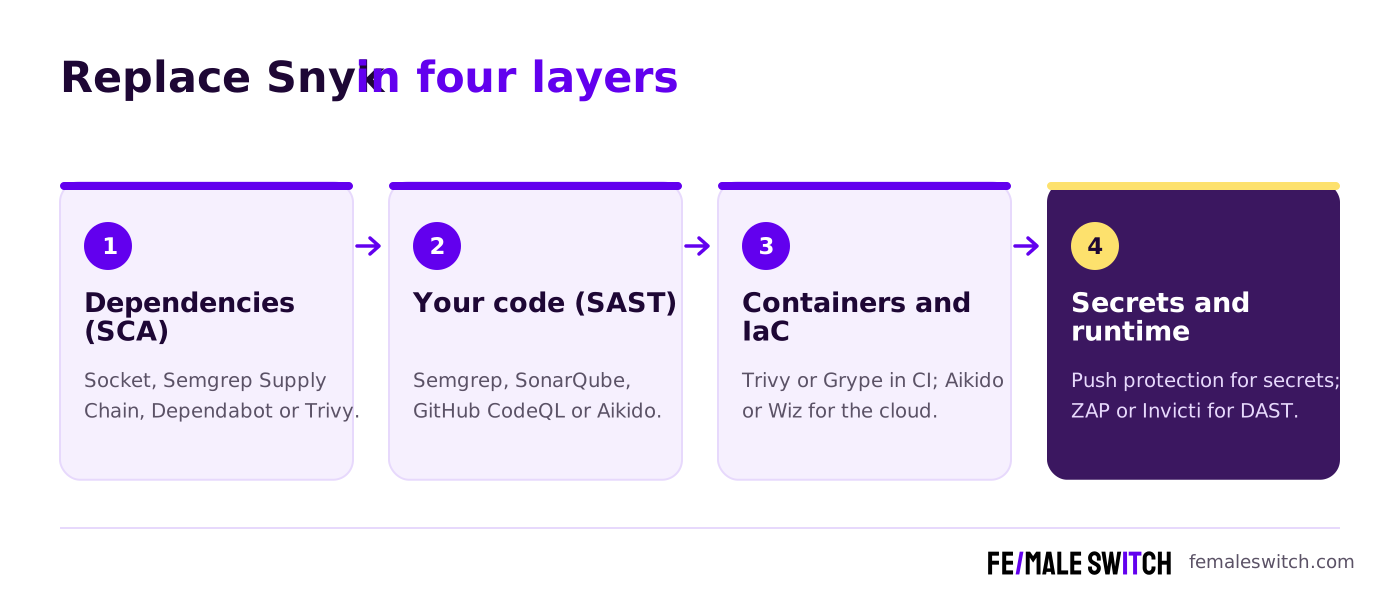
Quick answer: for most startups the best Snyk alternative is Aikido Security, which bundles SCA, SAST, secrets, cloud and DAST scanning with a free plan. Pick Semgrep for fast, customisable code scanning, Socket to block malicious packages, GitHub Secret Protection and Code Security if you live on GitHub, SonarQube for code quality plus security, and Trivy or Grype for free container and dependency scanning. Enterprises usually shortlist Checkmarx One, Veracode, Mend.io and Wiz.
Boost Your SEO by Getting Featured in Our Blogs and get a backlink.
We publish content about startups, education, tech, funding, etc. that ranks well not only in Google but also in Perplexity, ChatGPT, Grok and other AI tools.
👉 Get featured now!
What Snyk Offers and Costs in 2027
According to Snyk's pricing page, the Free plan costs $0 a month and covers SCA (Snyk Open Source), SAST (Snyk Code), IaC and container scanning, with real-time code scanning and integrations for IDEs, the CLI and source code managers. Its limits are 200 Open Source tests, 100 Code tests, 300 IaC tests and 100 Container tests. The Team plan starts at $25 a month, billed monthly, for teams of up to 10 developers, and adds higher test limits, Jira integration and next-business-day support.
Above that, Snyk sells an Enterprise Platform Subscription paid in prepaid credits (1 credit = $1), with each capability drawing from the balance at a daily rate per active contributor; you contact sales for a quote. Its newer Evo AI capabilities, such as AI pentesting and coding-agent security, are only available on Enterprise. Snyk also sells a DAST product called Snyk API & Web. Snyk counts a contributing developer as anyone who committed to a monitored private repository in the last 90 days, so costs grow with your team.
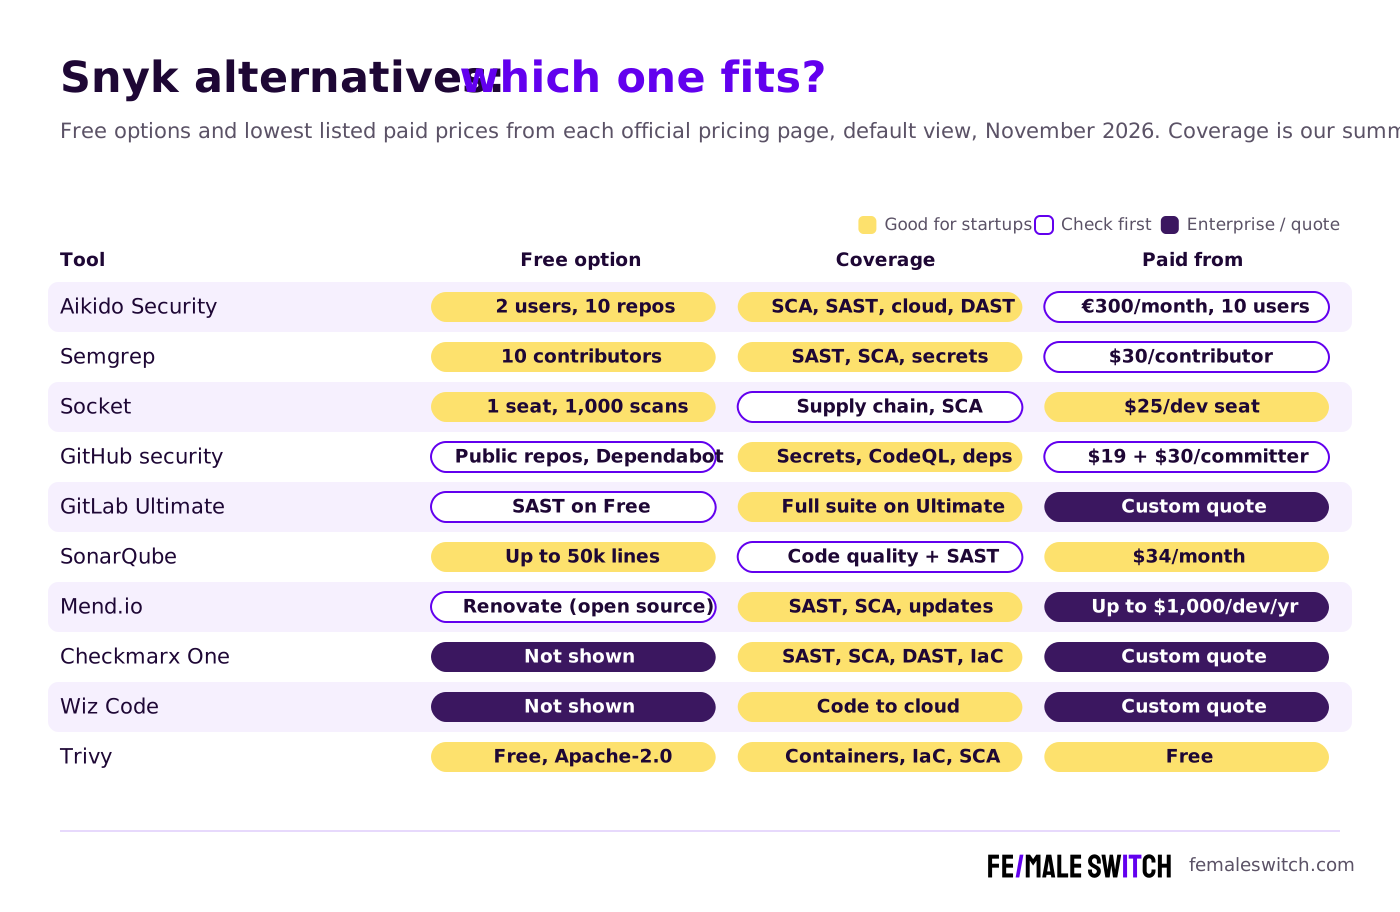
Snyk Alternatives Compared
Sources: each vendor's official pricing page (default view) and each project's official repository, checked 8 November 2026. Aikido showed prices in EUR from our location. Prices change often; check before you buy.
The Best Snyk Alternatives in 2027
1. Aikido Security: the all-in-one pick for startups
Aikido Security is the closest like-for-like Snyk replacement for small teams: dependency scanning (SCA) with reachability and licence checks, SAST and AI SAST, secrets detection, cloud misconfiguration checks (CSPM), container and IaC scanning and DAST in one dashboard. Its free Developer plan costs €0 forever and includes 2 users, 10 repos, 2 container images, 1 domain and 1 cloud account. Basic costs €300 a month in total for 10 users and adds PR security reviews, Jira and Linear sync and compliance syncs with Drata and Vanta. Aikido offers startups up to 30% off if they have raised less than 1.5M and have fewer than 10 team members.
2. Semgrep: fast, customisable code scanning
Semgrep is built around a fast static-analysis engine whose rules look like the code you are searching for, so your team can write its own checks. The free plan covers Semgrep Code (SAST) and Supply Chain (SCA) for up to 10 contributors and 10 private repositories, with cross-file analysis and 60 AI credits. Teams pricing starts at $30 per contributor a month for Code or Supply Chain and $15 for Secrets. The core engine, Semgrep Community Edition, is open source under LGPL-2.1 and released new versions in November 2026.
3. Socket: stop malicious packages before install
Socket focuses on supply-chain attacks: typosquats, malware and risky behaviour in open-source packages, which classic CVE scanners miss. The free plan gives 1 dev seat, 1,000 scans a month, unlimited private repositories and automatic blocking of malicious dependencies. Team costs $25 per dev seat a month (from 5 seats) and adds reachability analysis and Slack alerts; Business costs $50 per seat (from 20 seats). Many teams pair Socket with a SAST tool rather than replacing Snyk with it alone.
4. GitHub Secret Protection and Code Security
GitHub no longer sells one Advanced Security bundle to new teams. Its security plans page lists two add-ons: Secret Protection at $19 per active committer a month (secret scanning, push protection, validity checks, custom patterns) and Code Security at $30 per active committer a month (CodeQL code scanning, Copilot Autofix and more). Secret scanning, push protection and CodeQL are free for public repositories, and Dependabot security and version updates are included on every plan. If your code is on GitHub, this is the simplest answer to "Snyk vs GitHub Advanced Security": free Dependabot covers basic SCA, and you add the paid features only for private repos.
5. GitLab Ultimate: security built into the DevSecOps platform
On GitLab, the Free plan already includes static application security testing (SAST) for up to 5 users per top-level group. Premium costs $29 per user a month billed annually, while the full application security testing, software supply chain security and vulnerability management suite sits in Ultimate, which has custom pricing. It makes sense when your repos and CI already live in GitLab.
Validate your startup idea with the unique borrowed authority approach: we publish articles about your product in our blog and you get traffic and testers for your MVP
- Prove Market Demand: See real organic traffic and waitlist conversions
- Unlock High-Potential Keywords: Receive a curated list of top-performing keywords directly from Google Search Console data.
- Estimate Customer Acquisition Cost (CAC): Gain financial foresight with an estimated CAC based on real keyword performance data.
🔗 Start validating your startup now
6. SonarQube: code quality and security together
SonarQube from Sonar finds bugs, vulnerabilities and security hotspots in more than 35 languages on every pull request. Its free tier covers private projects up to 50,000 lines of code, and public OSI-licensed open-source projects get it free. The Team plan starts at $34 a month for up to 100,000 lines of code (for teams under 50 developers). Deeper SAST and SCA (CVEs, malicious packages, SBOM, licence policy) come with SonarQube Advanced Security. Choose it if you want one tool for clean code and security.
7. Mend.io: enterprise SCA, SAST and dependency updates
Mend.io (formerly WhiteSource) lists Mend AppSec at up to $1,000 per developer a year for SAST, SCA, AI-generated code security and automated dependency updates, and Mend Renovate Enterprise at up to $250. Its dependency-update bot Renovate is open source (AGPL-3.0) and free to self-host, a good first step even if you never buy the platform.
8. Checkmarx One: a broad enterprise suite
Checkmarx One offers SAST, SCA, DAST, API, container, IaC and secrets scanning, with Essentials, Professional and Enterprise packages that all need a custom quote. It fits larger engineering teams with compliance requirements more than a two-person startup.
9. Veracode: SAST, DAST and SCA for regulated companies
Veracode covers SAST, DAST, SCA, container security and a package firewall, with a Risk Manager (ASPM) view, security training and penetration testing as a service. Prices are not public, so you request a demo. Choose it when customers or auditors expect an established enterprise AppSec vendor.
10. Wiz Code: code-to-cloud security, now part of Google Cloud
Wiz Code connects code, cloud and runtime findings so you see which vulnerabilities are really exploitable, with feedback in pull requests, IDEs and pipelines. Google completed its acquisition of Wiz on 11 March 2026; Wiz joined Google Cloud and keeps its brand, and Google says Wiz products continue to work across all major clouds. Pricing is a custom quote. It suits cloud-heavy companies more than early-stage teams.
11. JFrog Xray and Advanced Security
If your packages and containers already go through Artifactory, JFrog can scan them where they are stored. In the SaaS default view, code and binary SCA, JFrog Advanced Security and Curation come with the Enterprise X plan, which starts at $950 a month.
12. Invicti: DAST for web apps and APIs
Invicti (formerly Netsparker) is best known for DAST, which tests running web apps and APIs, and is now a platform with SAST, SCA, secrets and ASPM. Its AppSec Core plan is sold through a demo, and its agentic pentest for a single application is listed at $500 maximum per pentest. Use it alongside, not instead of, a code and dependency scanner.
Free and Open-Source Snyk Alternatives
Looking for alternatives to Snyk that are open source? These four are free, Apache-2.0 licensed and released new versions within the last year (checked on their official repositories in November 2026):
- Trivy (by Aqua Security): one scanner for CVEs and IaC misconfigurations across code repositories, binaries, container images and Kubernetes clusters; the most complete free replacement for Snyk Container and Snyk IaC.
- Grype (by Anchore): a vulnerability scanner for container images and file systems.
- OWASP Dependency-Check: one of the earliest SCA tools, with a CLI and Maven, Gradle, Ant, Jenkins, GitHub Actions and Azure DevOps integrations. Its code moved to the dependency-check organisation on GitHub; the old repository is archived.
- ZAP: the free web app scanner (DAST), now branded ZAP by Checkmarx while it remains an independent open-source project.
Discontinued or Changed Since the Old Version of This Page
- SOOS: its website now says SOOS.io has shut down and the service no longer exists, so it is removed from the list.
- GitHub Advanced Security: now sold as two add-ons, Secret Protection and Code Security (see above).
- Wiz: now part of Google Cloud after the acquisition closed in March 2026.
- OWASP ZAP: now ZAP by Checkmarx, still free and open source.
- Snyk: enterprise pricing is now a credit-based platform subscription, and Snyk also sells DAST (Snyk API & Web) and Evo AI security features.
Which Snyk Alternative Should You Choose?
- You want one affordable tool for everything: Aikido Security.
- Your code is on GitHub: free Dependabot plus GitHub Code Security and Secret Protection for private repos.
- Your code is on GitLab: GitLab's built-in SAST, then Ultimate when you need the full suite.
- You want custom rules and fast CI scans: Semgrep.
- You worry about malicious npm or PyPI packages: Socket.
- You care about code quality as much as security: SonarQube.
- You need zero cost: Trivy, Grype, OWASP Dependency-Check and ZAP in your CI pipeline.
- You sell to enterprises with strict audits: Checkmarx One, Veracode, Mend.io or Wiz.
How Founders Use Security Scanning
Security questionnaires arrive the moment you sell to a bigger customer, so a basic scanning setup pays for itself early. A sensible startup stack is a free SCA scanner in CI, a SAST tool on every pull request and secret push protection from day one. If you build fast with AI coding tools, scanning matters even more: compare the GitHub Copilot alternatives and open-source GitHub Copilot alternatives, learn how to prototype a SaaS with AI coding and read our guide to AI-powered MVP development.
Internal tools and automations need the same care. If you self-host, check our open-source Retool alternatives, open-source Mendix alternatives, open-source Zapier alternatives, open-source Stripe alternatives and open-source Google Analytics alternatives, and draw your architecture and threat model with the open-source PlantUML alternatives.
To go deeper, read the cybersecurity startup lessons, the steps to secure enterprise systems, the guide to secure data collaboration, our list of cybersecurity experts in the Netherlands and the top cybersecurity startup events. Validate the product first with the 30-day validation sprint, and once it is live, the F/MS AI SEO Tool helps customers find it in Google and AI assistants.
Join ElonaHunt (like ProductHunt but for women) and explore the coolest women-focused startups out there!
Discover your next big inspiration and connect with like-minded female entrepreneurs!
👉 Join the Hunt Here
FAQ About Snyk Alternatives
What is the best alternative to Snyk?
For most startups, Aikido Security: it bundles SCA, SAST, secrets, cloud and DAST scanning and has a free plan for 2 users and 10 repos. Semgrep is the best choice if you want custom code-scanning rules.
Who are Snyk's main competitors?
Aikido Security, Semgrep, Socket, GitHub Code Security and Secret Protection, GitLab Ultimate, SonarQube, Mend.io, Checkmarx, Veracode, Wiz, JFrog and Invicti, plus the open-source scanners Trivy, Grype, OWASP Dependency-Check and ZAP.
Is there a free alternative to Snyk?
Yes. Trivy, Grype, OWASP Dependency-Check and ZAP are free and open source. Aikido, Semgrep, Socket and SonarQube also have free plans, and GitHub includes Dependabot updates on every plan.
What are the best open-source Snyk alternatives?
Trivy for containers, IaC and dependencies, Grype for container images, OWASP Dependency-Check for SCA in builds, ZAP for DAST and Semgrep Community Edition (LGPL-2.1) for code scanning.
How much does Snyk cost?
Snyk's Free plan costs $0 with limits of 200 Open Source, 100 Code, 300 IaC and 100 Container tests. Team starts at $25 a month billed monthly for up to 10 developers, and Enterprise uses prepaid credits at $1 per credit through sales.
Snyk vs GitHub Advanced Security: which is better?
If your code is on GitHub, GitHub's add-ons are simpler: Secret Protection costs $19 and Code Security $30 per active committer a month, and Dependabot is free. Snyk works with several source code managers and puts container and IaC scanning in the same dashboard.
Aikido Security vs Snyk: what is the difference?
Aikido bundles cloud posture checks, DAST and runtime protection with code and dependency scanning, and prices per team (Basic €300 a month for 10 users). Snyk prices Team per month for up to 10 developers and moves bigger customers to credits.
What's a good Snyk alternative for a team that has outgrown free-tier limits?
Semgrep Teams ($30 per contributor a month), Socket Team ($25 per dev seat), Aikido Basic (€300 a month for 10 users) or SonarQube Team (from $34 a month) are the usual next steps, or self-host Trivy and Grype in CI.
What happened to SOOS?
SOOS has shut down: its website says SOOS.io no longer exists. Former users can look at Aikido, Socket or Semgrep for SCA, and ZAP or Invicti for DAST.
Where can I get a backlink by writing about my startup?
You can publish a guest post in one of the Fe/male Switch startup blogs, which rank in Google and in AI tools. Get a quality backlink.
About the Author
Violetta Bonenkamp, also known as MeanCEO, is an experienced startup founder with an impressive educational background including an MBA and four other higher education degrees. She has over 20 years of work experience across multiple countries, including 5 years as a solopreneur and serial entrepreneur. Throughout her startup experience she has applied for multiple startup grants at the EU level, in the Netherlands and Malta, and her startups received quite a few of those. She’s been living, studying and working in many countries around the globe and her extensive multicultural experience has influenced her immensely.